AutoPWN Suite
Point it at a network and it finds the hosts, works out what software they run, looks up the CVEs that apply and downloads public exploits for them. A command line tool, a web dashboard and a Python library.
I'm Kaan, from Çanakkale, Türkiye. I came to security from the offensive side, through CTFs and BadUSB experiments, and I've been building tools ever since: from AutoPWN Suite, the vulnerability scanner I started in 2022, to a live bus tracker for Çanakkale and FundHunter, an investment fund analysis and portfolio tracking app.
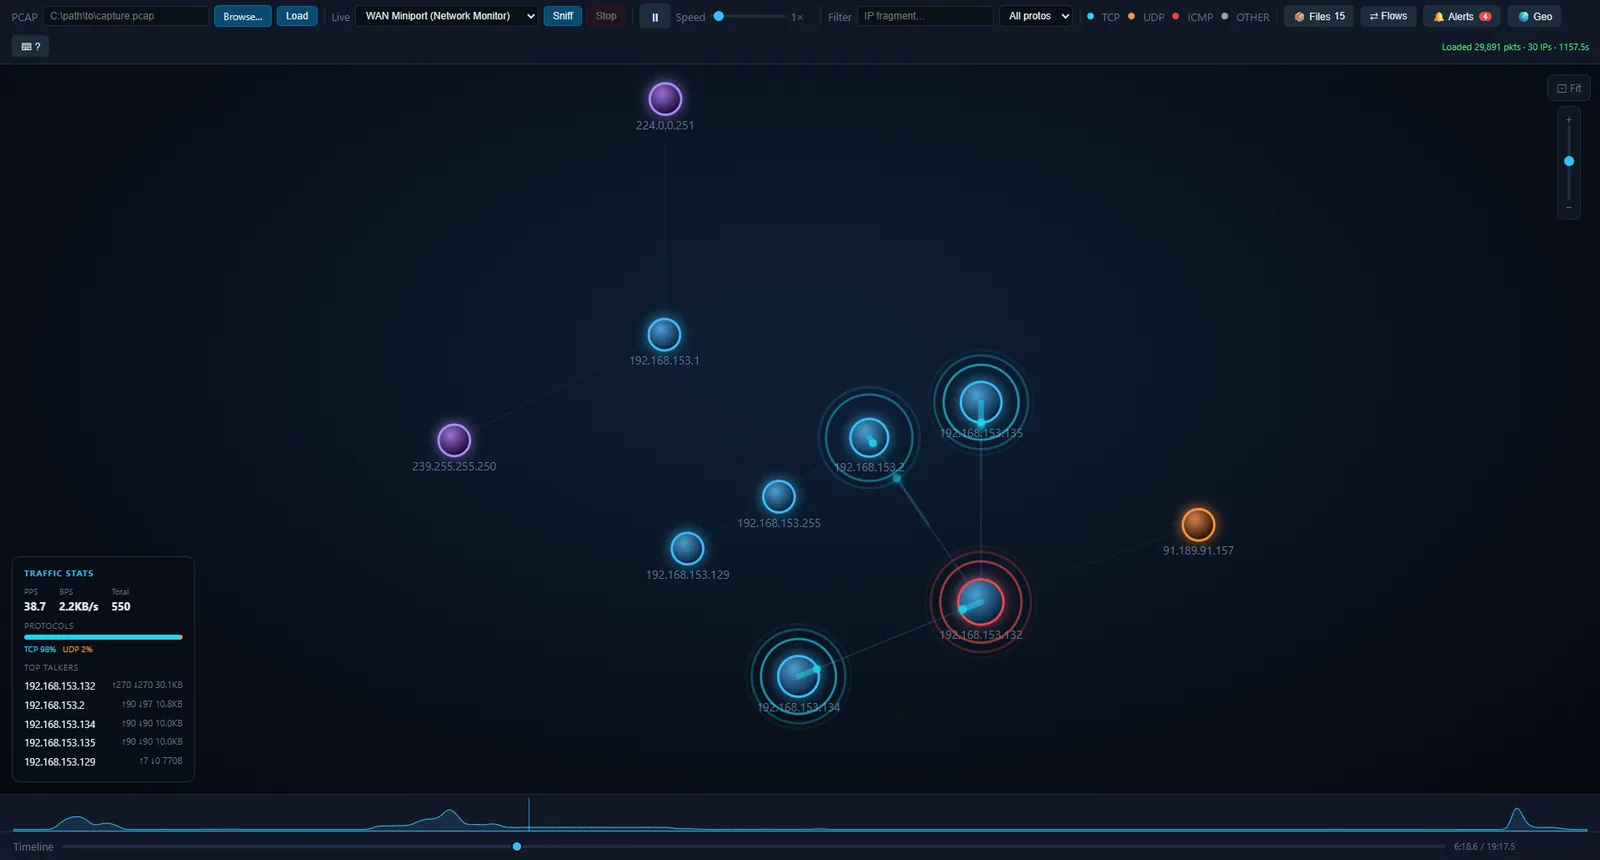
Security tools, and things I wanted and couldn't find: a bus app for my city, a way to see what Turkish investment funds actually hold, a packet capture you can watch.
Point it at a network and it finds the hosts, works out what software they run, looks up the CVEs that apply and downloads public exploits for them. A command line tool, a web dashboard and a Python library.
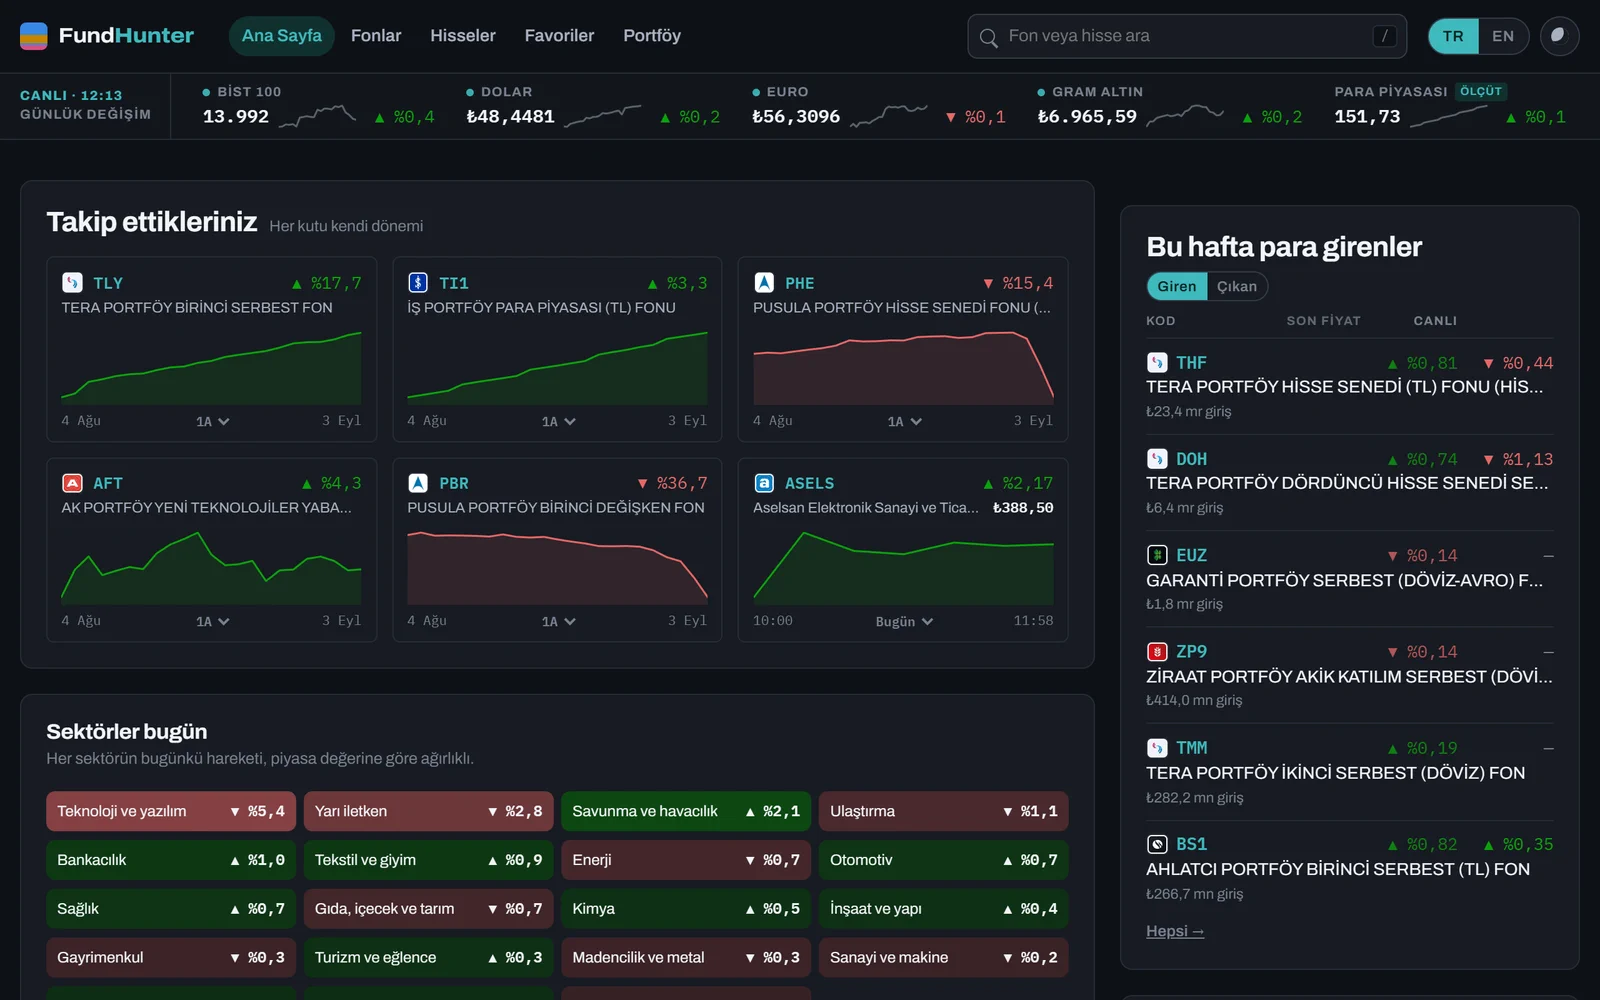
Every investment fund in Türkiye and what it actually holds: 2,063 funds and 648 Borsa İstanbul listings, read out of their monthly filings. Runs entirely in the browser.
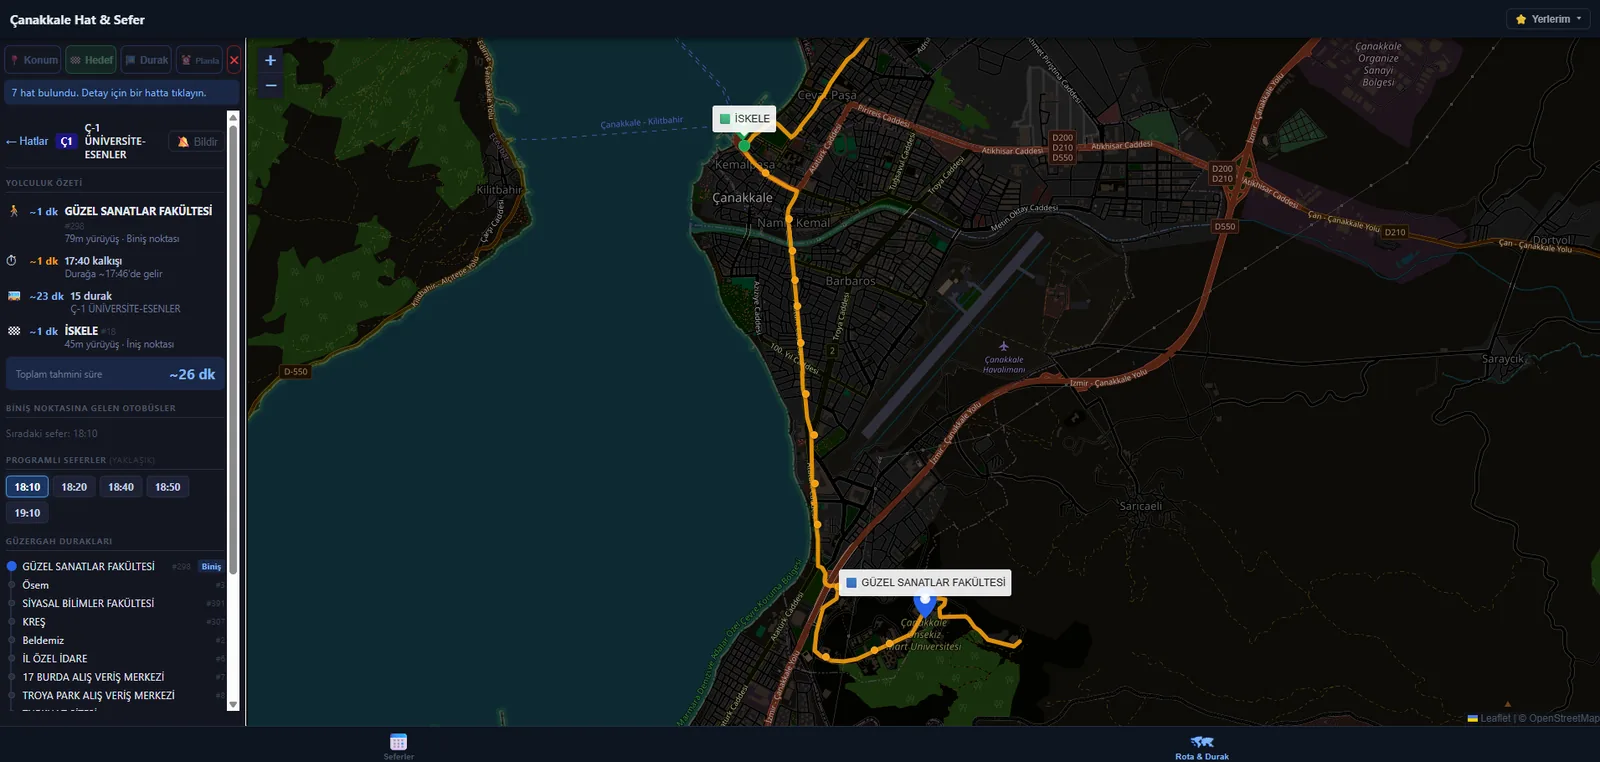
Çanakkale’s buses have no official app, so I made one: live bus positions, a trip planner, the municipality’s PDF timetables turned into something usable, and alerts when your bus is close.
Founding engineer. SolonGate sits between AI agents and the tools they call, allows or blocks each call against a policy on the user's own machine, and records every decision in an audit trail. It also catches secrets and personal data before someone pastes them into a chatbot.
Most of this autumn went into making it trustworthy rather than bigger: a login for the dashboard, signed releases, a public write-up of every issue a security review found, and CVE matching that reads NVD's version ranges instead of grepping descriptions.
Both are live and still get regular commits. Their data refreshes on its own, every day for FundHunter and every hour for the Çanakkale bus timetables.
The most effective way to build resilient defenses is to deeply understand and simulate modern attack vectors. Offensive research directly fuels defensive strategy.
Automating repetitive work frees human expertise for creative problem-solving. Good tooling lets security people focus on what matters.
Sharing knowledge and tools raises the bar for everyone. I contribute to projects that make security more accessible and more effective.
The next certificate on my list, to formalise the fundamentals.
Voice commands, device control and some computer vision over the machines and ESP32 boards I already have running. Slowly.